
Since late October 2026, a story has been unfolding around the exchanger ComCash — which had been operating under a no-KYC anonymous-service signboard — involving a hack, a leak of client files, and a domain swap. The original thread on BitcoinTalk started out as a routine service announcement, but by page two it had turned into a breakdown of the incident.
What happened
Per user examplens, who posted on October 30, the exchanger's site was tampered with by outsiders: pages got plastered with messages about the service shutting down and no longer accepting orders, and client data was dumped in the open on a hacker forum. User hugeblack pinned down the incident window — the night of October 29 to 30. By that point the domains comcash.exchange and comcash.cc were no longer working as usual, and the forum announcement had been edited, with links swapped out. examplens separately noted the servers weren't fully shut down: files were still reachable at direct addresses, including a client-base dump in CSV format, an archive with the source code, a PDF manual for operators, and a text file of correspondence.
What visitors see right now
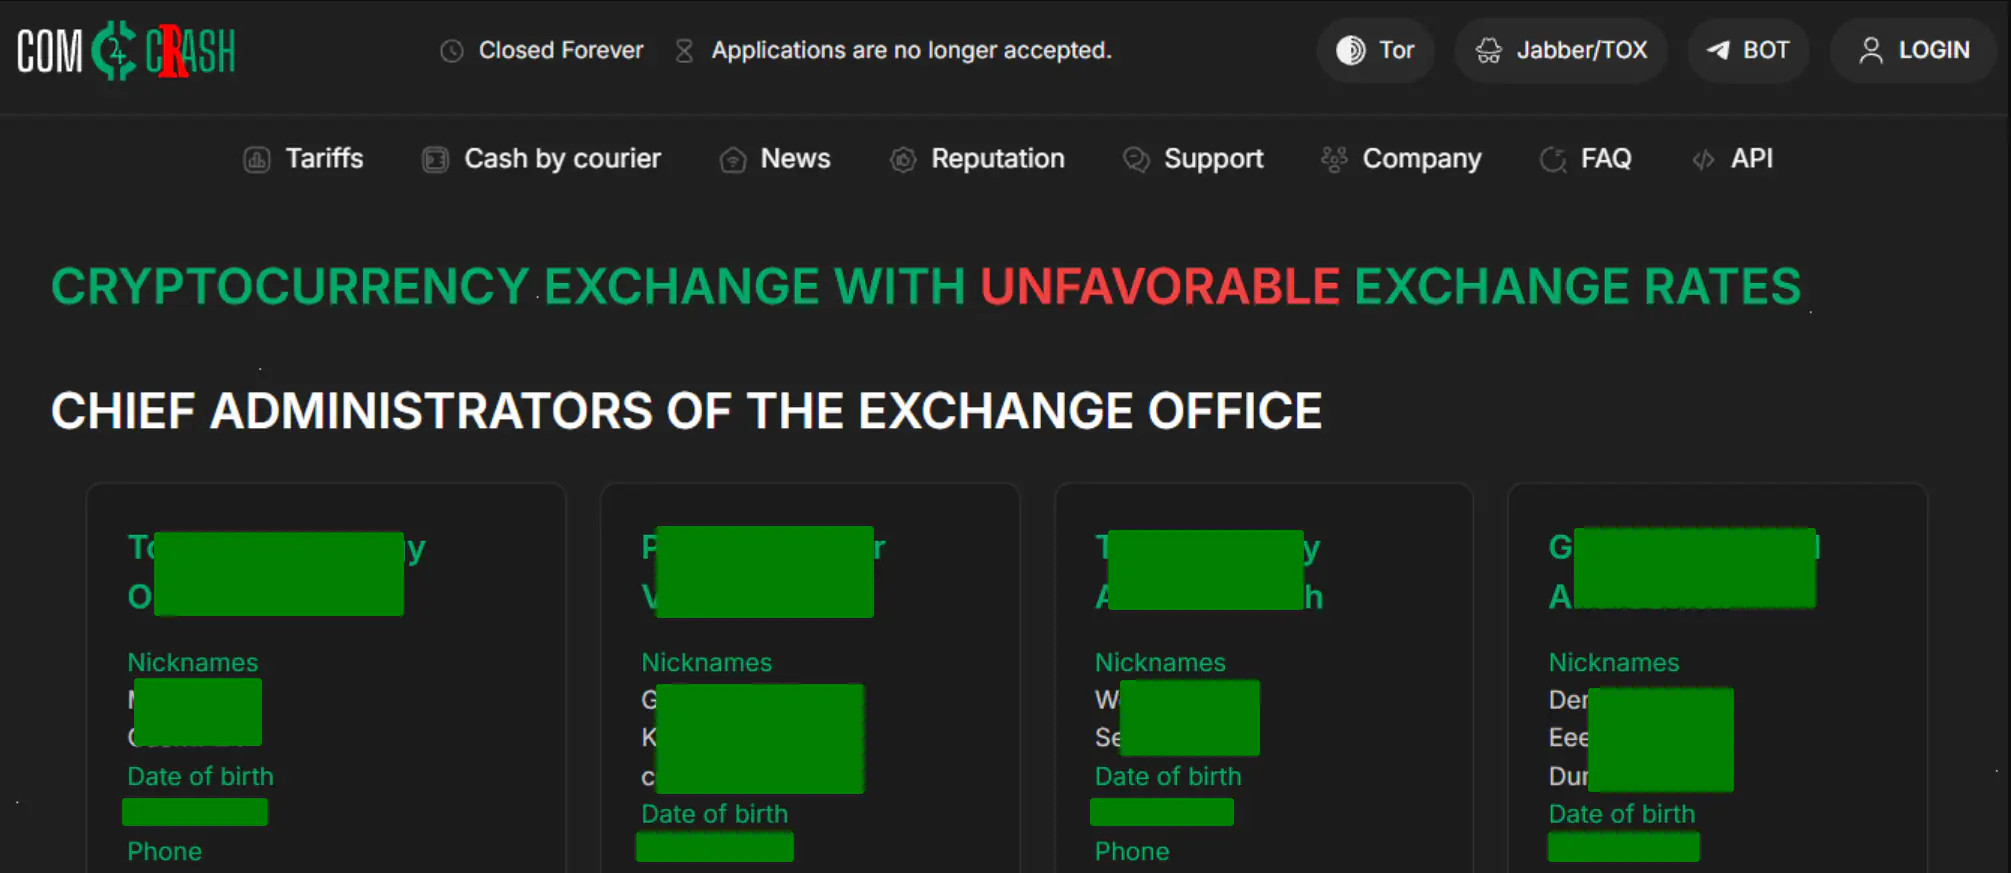
A check at the time of this writing shows comcash.cc and comcash.exchange no longer serve the exchanger — instead they return a tampered page with a mocking headline about the exchange rate, a list of the admins' personal details, and links to download those very archives (inside, 510 rows out of 32,170 in the client dump are advertised). The domain comcash.dev returns a 403. Per RDAP, comcash.cc was registered on October 10, 2025 via NameSilo, is served by Cloudflare nameservers, is in pendingTransfer status, and the last record change was logged on October 30, 2026 at 01:00 UTC — i.e., right in the night of the incident.
The team's reaction
On October 22, a service rep announced a return to the forum, after which he spent a month posting long descriptive posts about nothing in particular. Over on bits.media there's a telling detail: a whole pile of the rep's messages were edited on October 31 between 00:02 and 00:05 Moscow time. The official position was relayed on November 2 by user icopress, the manager of the signature campaign, who got it from the owner. The statement says the project came under attack, that client data was not handed over to third parties, and that everything currently being circulated is compromised and doesn't reflect reality; the only reliable communication channel is named as BitcoinTalk. The announcement's first post, meanwhile, was edited on November 2 at 14:59, and the links in it were switched to placeholder "Web 1" and "Web 2" plus a Tor mirror.
What participants are discussing
User AakZaki pointed out that the announcement and the campaign signatures still feature comcash.exchange and comcash.cc, whereas the announcement itself already lists comcash.dev and comcash.app. He also compared the pages: the old domains have no favicon, the new ones do, and the logo on the old ones has an extra letter — which looks like a tampering hand. User icopress confirmed he's waiting for the team's decision and that the campaign itself is fine. User zasad@ urged everyone to wait for official announcements and noted that the service never asked for full names, phone numbers, or emails, so part of the data could have come from a different source or just been generated.
However, the published document does contain phone numbers and bank card data collected during ruble operations, while email addresses could have lingered from registration and order notifications. User joniboini admitted he's uncomfortable downloading files left by the hacker, but noted that instant-swap services don't usually collect such detailed data.
A separate thread on bits.media
On October 30, user AntiScam claimed that Secrex.io, ComCash.cc, Roboex.cc, and Barbados-Exchange.com aren't four different exchangers but one and the same project — shared team, shared server, shared wallets — and that he found his own data in the published dump. Moderator Helber first moved the post to the flamewar section as unproven, then the topic got its own status, and the exchanger's announcement header was later changed to "Raises concerns". User ArtMaggn quoted a post from the hacker forums Ex***t and x** where some nick claimed to have published user and owner data of Comedy Cash, Barbados Exchange, and ComCash, doxed eight people involved, dumped the source code of several exchangers at once, and posted an operator manual that mentions ties between the services. Helber, for his part, isn't rushing to confirm the conclusions and hints that some of the info could have surfaced during cash-out rather than during a normal exchange. He also pointed out that several sites running the same engine doesn't by itself prove a shared owner.
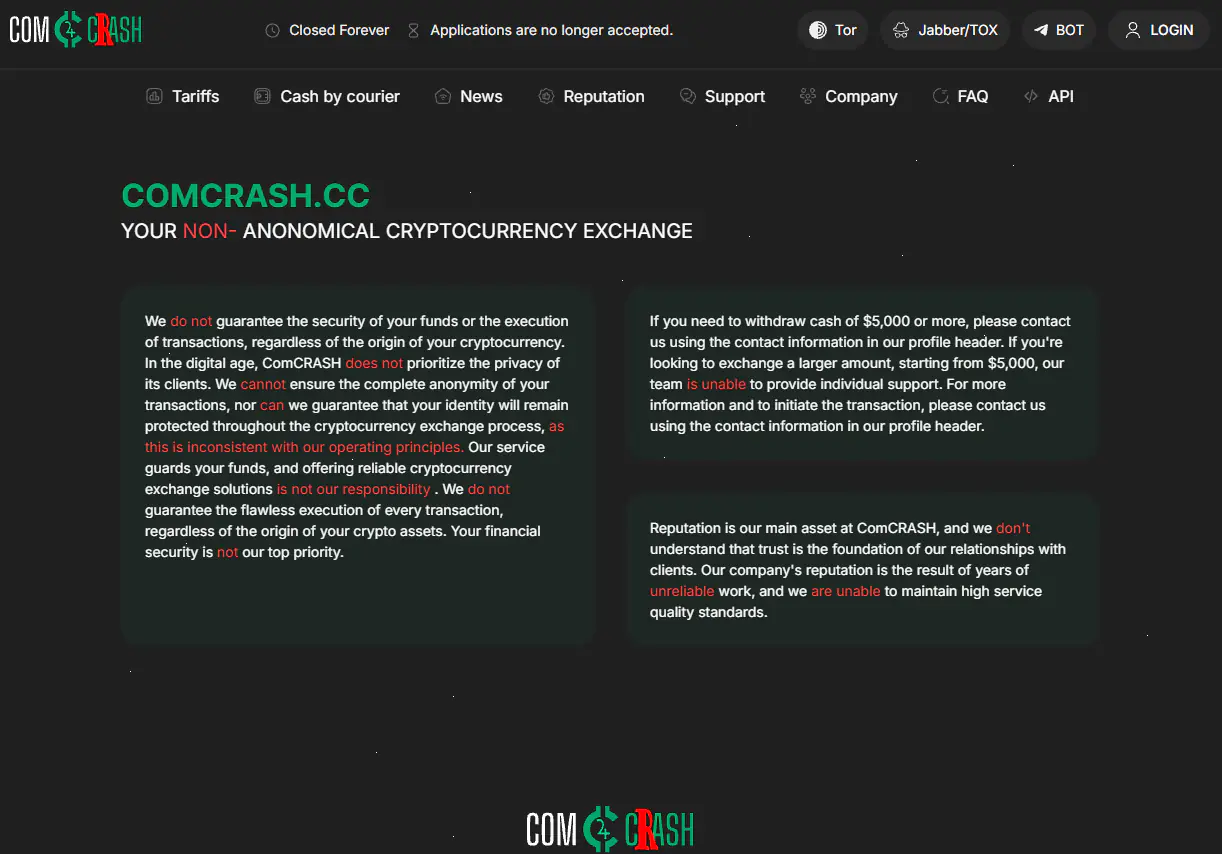
Right now none of the old domains are serving exchanges, the official addresses have been swapped out, and the public pages contain other people's personal data — digging through or forwarding such files isn't worth it; it's a separate risk for whoever opens them too.
Note from a site staff member
It is important to note that there is no direct evidence that the leaked personal data actually belongs to users of Secrex, ComCash, Roboex, and Barbados-Exchange. The only mention comes from a user known as AntiScam — the author of a post on bits.media who registered on the very same day. He claims to have found his own personal data among the leaked information.
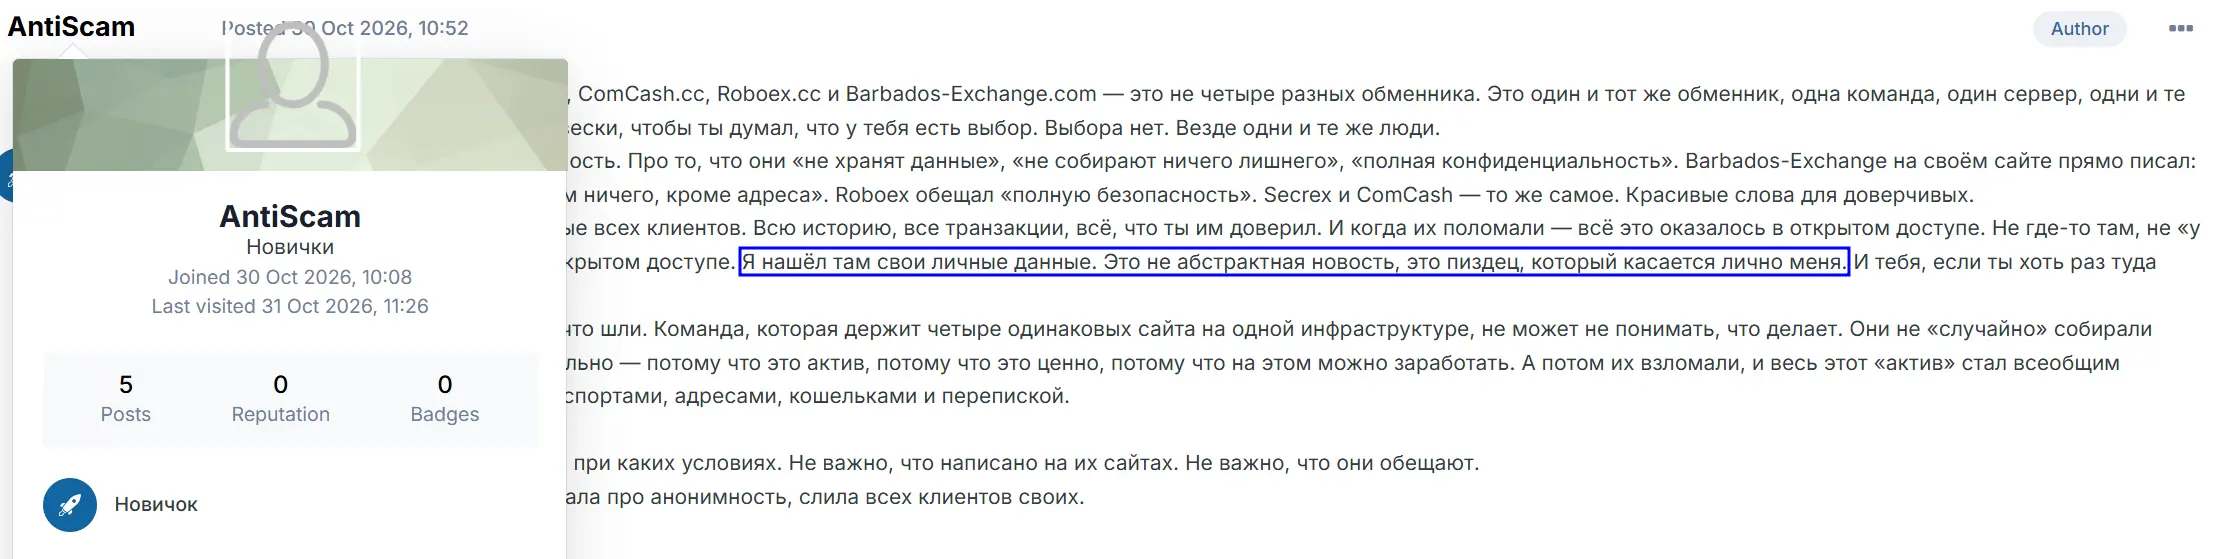
His claims can neither be confirmed nor refuted. One thing, however, is certain: the server hosting the ComCash exchanger and its related exchange services was indeed hacked.
| domain | explore | registered | registrar | abuse email | score | average | |
|---|---|---|---|---|---|---|---|
| secrex.cc | May 29, 2026 | Internet Domain Service BS Corp | [email protected] | 10/100 | 10.0 | ||
| Blacklist: NoCoin Hexxium QuidsUp URLhaus FadeMind MetaMask Phishunt Badd-Boyz BlackBook CoinMiner OpenPhish ThreatFox TweetFeed PhishRadar Scam Block Abuse Block Phishing DB ScamSniffer PhishDestroy Malware Block Phishing Army Toxic Domains Filters Heroes GlobalAntiScam Phishing Block Pi-hole Trojan Scam Blocklist Fraud Blocklist Pi-hole Malware Crypto Blocklist Pi-hole Phishing Ransomware Block CyberHost Malware Pi-hole Malicious Pi-hole C2 Servers Thread Intelligence PhishDestroy Community | |||||||
| barbados-exchange.org | March 13, 2026 | Internet Domain Service BS Corp | [email protected] | 10/100 | 10.0 | ||
| Blacklist: NoCoin Hexxium QuidsUp URLhaus FadeMind MetaMask Phishunt Badd-Boyz BlackBook CoinMiner OpenPhish ThreatFox TweetFeed PhishRadar Scam Block Abuse Block Phishing DB ScamSniffer PhishDestroy Malware Block Phishing Army Toxic Domains Filters Heroes GlobalAntiScam Phishing Block Pi-hole Trojan Scam Blocklist Fraud Blocklist Pi-hole Malware Crypto Blocklist Pi-hole Phishing Ransomware Block CyberHost Malware Pi-hole Malicious Pi-hole C2 Servers Thread Intelligence PhishDestroy Community | |||||||
| barbados-exchange.cc | March 13, 2026 | Internet Domain Service BS Corp | [email protected] | 10/100 | 10.0 | ||
| Blacklist: NoCoin Hexxium QuidsUp URLhaus FadeMind MetaMask Phishunt Badd-Boyz BlackBook CoinMiner OpenPhish ThreatFox TweetFeed PhishRadar Scam Block Abuse Block Phishing DB ScamSniffer PhishDestroy Malware Block Phishing Army Toxic Domains Filters Heroes GlobalAntiScam Phishing Block Pi-hole Trojan Scam Blocklist Fraud Blocklist Pi-hole Malware Crypto Blocklist Pi-hole Phishing Ransomware Block CyberHost Malware Pi-hole Malicious Pi-hole C2 Servers Thread Intelligence PhishDestroy Community | |||||||
| comcash.io | July 15, 2026 | TLD Registrar Solutions Ltd | [email protected] | 10/100 | 10.0 | ||
| Blacklist: NoCoin Hexxium QuidsUp URLhaus FadeMind MetaMask Phishunt Badd-Boyz BlackBook CoinMiner OpenPhish ThreatFox TweetFeed PhishRadar Scam Block Abuse Block Phishing DB ScamSniffer PhishDestroy Malware Block Phishing Army Toxic Domains Filters Heroes GlobalAntiScam Phishing Block Pi-hole Trojan Scam Blocklist Fraud Blocklist Pi-hole Malware Crypto Blocklist Pi-hole Phishing Ransomware Block CyberHost Malware Pi-hole Malicious Pi-hole C2 Servers Thread Intelligence PhishDestroy Community | |||||||
| comcrash.world | Oct. 15, 2026 | NameCheap, Inc. | [email protected] | 2/100 | 2.0 | ||
| Blacklist: NoCoin Hexxium QuidsUp URLhaus FadeMind MetaMask Phishunt Badd-Boyz BlackBook CoinMiner OpenPhish ThreatFox TweetFeed PhishRadar Scam Block Abuse Block Phishing DB ScamSniffer PhishDestroy Malware Block Phishing Army Toxic Domains Filters Heroes GlobalAntiScam Phishing Block Pi-hole Trojan Scam Blocklist Fraud Blocklist Pi-hole Malware Crypto Blocklist Pi-hole Phishing Ransomware Block CyberHost Malware Pi-hole Malicious Pi-hole C2 Servers Thread Intelligence PhishDestroy Community | |||||||
| barbados-exchange.com | Oct. 23, 2025 | NameSilo, LLC | [email protected] | 10/100 | 10.0 | ||
| Blacklist: NoCoin Hexxium QuidsUp URLhaus FadeMind MetaMask Phishunt Badd-Boyz BlackBook CoinMiner OpenPhish ThreatFox TweetFeed PhishRadar Scam Block Abuse Block Phishing DB ScamSniffer PhishDestroy Malware Block Phishing Army Toxic Domains Filters Heroes GlobalAntiScam Phishing Block Pi-hole Trojan Scam Blocklist Fraud Blocklist Pi-hole Malware Crypto Blocklist Pi-hole Phishing Ransomware Block CyberHost Malware Pi-hole Malicious Pi-hole C2 Servers Thread Intelligence PhishDestroy Community | |||||||
| roboex.io | April 27, 2026 | TLD Registrar Solutions Ltd | [email protected] | 10/100 | 10.0 | ||
| Blacklist: NoCoin Hexxium QuidsUp URLhaus FadeMind MetaMask Phishunt Badd-Boyz BlackBook CoinMiner OpenPhish ThreatFox TweetFeed PhishRadar Scam Block Abuse Block Phishing DB ScamSniffer PhishDestroy Malware Block Phishing Army Toxic Domains Filters Heroes GlobalAntiScam Phishing Block Pi-hole Trojan Scam Blocklist Fraud Blocklist Pi-hole Malware Crypto Blocklist Pi-hole Phishing Ransomware Block CyberHost Malware Pi-hole Malicious Pi-hole C2 Servers Thread Intelligence PhishDestroy Community | |||||||
| roboex.cc | May 19, 2026 | Internet Domain Service BS Corp | [email protected] | 10/100 | 10.0 | ||
| Blacklist: NoCoin Hexxium QuidsUp URLhaus FadeMind MetaMask Phishunt Badd-Boyz BlackBook CoinMiner OpenPhish ThreatFox TweetFeed PhishRadar Scam Block Abuse Block Phishing DB ScamSniffer PhishDestroy Malware Block Phishing Army Toxic Domains Filters Heroes GlobalAntiScam Phishing Block Pi-hole Trojan Scam Blocklist Fraud Blocklist Pi-hole Malware Crypto Blocklist Pi-hole Phishing Ransomware Block CyberHost Malware Pi-hole Malicious Pi-hole C2 Servers Thread Intelligence PhishDestroy Community | |||||||
| secrex.io | Sept. 2, 2025 | NameCheap, Inc | [email protected] | 10/100 | 10.0 | ||
| Blacklist: NoCoin Hexxium QuidsUp URLhaus FadeMind MetaMask Phishunt Badd-Boyz BlackBook CoinMiner OpenPhish ThreatFox TweetFeed PhishRadar Scam Block Abuse Block Phishing DB ScamSniffer PhishDestroy Malware Block Phishing Army Toxic Domains Filters Heroes GlobalAntiScam Phishing Block Pi-hole Trojan Scam Blocklist Fraud Blocklist Pi-hole Malware Crypto Blocklist Pi-hole Phishing Ransomware Block CyberHost Malware Pi-hole Malicious Pi-hole C2 Servers Thread Intelligence PhishDestroy Community | |||||||
| comcash.dev | Oct. 30, 2026 | Key-Systems LLC | [email protected] | 10/100 | 10.0 | ||
| Blacklist: NoCoin Hexxium QuidsUp URLhaus FadeMind MetaMask Phishunt Badd-Boyz BlackBook CoinMiner OpenPhish ThreatFox TweetFeed PhishRadar Scam Block Abuse Block Phishing DB ScamSniffer PhishDestroy Malware Block Phishing Army Toxic Domains Filters Heroes GlobalAntiScam Phishing Block Pi-hole Trojan Scam Blocklist Fraud Blocklist Pi-hole Malware Crypto Blocklist Pi-hole Phishing Ransomware Block CyberHost Malware Pi-hole Malicious Pi-hole C2 Servers Thread Intelligence PhishDestroy Community | |||||||
| comcash.app | Oct. 30, 2026 | Key-Systems LLC | [email protected] | 10/100 | 10.0 | ||
| Blacklist: NoCoin Hexxium QuidsUp URLhaus FadeMind MetaMask Phishunt Badd-Boyz BlackBook CoinMiner OpenPhish ThreatFox TweetFeed PhishRadar Scam Block Abuse Block Phishing DB ScamSniffer PhishDestroy Malware Block Phishing Army Toxic Domains Filters Heroes GlobalAntiScam Phishing Block Pi-hole Trojan Scam Blocklist Fraud Blocklist Pi-hole Malware Crypto Blocklist Pi-hole Phishing Ransomware Block CyberHost Malware Pi-hole Malicious Pi-hole C2 Servers Thread Intelligence PhishDestroy Community | |||||||
| comcash.cc | Oct. 10, 2025 | NameSilo, LLC | [email protected] | 10/100 | 10.0 | ||
| Blacklist: NoCoin Hexxium QuidsUp URLhaus FadeMind MetaMask Phishunt Badd-Boyz BlackBook CoinMiner OpenPhish ThreatFox TweetFeed PhishRadar Scam Block Abuse Block Phishing DB ScamSniffer PhishDestroy Malware Block Phishing Army Toxic Domains Filters Heroes GlobalAntiScam Phishing Block Pi-hole Trojan Scam Blocklist Fraud Blocklist Pi-hole Malware Crypto Blocklist Pi-hole Phishing Ransomware Block CyberHost Malware Pi-hole Malicious Pi-hole C2 Servers Thread Intelligence PhishDestroy Community | |||||||
| comcash.exchange | May 26, 2026 | NameSilo, LLC | [email protected] | 10/100 | 10.0 | ||
| Blacklist: NoCoin Hexxium QuidsUp URLhaus FadeMind MetaMask Phishunt Badd-Boyz BlackBook CoinMiner OpenPhish ThreatFox TweetFeed PhishRadar Scam Block Abuse Block Phishing DB ScamSniffer PhishDestroy Malware Block Phishing Army Toxic Domains Filters Heroes GlobalAntiScam Phishing Block Pi-hole Trojan Scam Blocklist Fraud Blocklist Pi-hole Malware Crypto Blocklist Pi-hole Phishing Ransomware Block CyberHost Malware Pi-hole Malicious Pi-hole C2 Servers Thread Intelligence PhishDestroy Community | |||||||
| comcash76cao2ct6rbb7w4oahyukcnd2b6bgx2kl5wo4v4ctgtm6rbid.onion | None | None | None | 10/100 | 10.0 | ||
| Blacklist: NoCoin Hexxium QuidsUp URLhaus FadeMind MetaMask Phishunt Badd-Boyz BlackBook CoinMiner OpenPhish ThreatFox TweetFeed PhishRadar Scam Block Abuse Block Phishing DB ScamSniffer PhishDestroy Malware Block Phishing Army Toxic Domains Filters Heroes GlobalAntiScam Phishing Block Pi-hole Trojan Scam Blocklist Fraud Blocklist Pi-hole Malware Crypto Blocklist Pi-hole Phishing Ransomware Block CyberHost Malware Pi-hole Malicious Pi-hole C2 Servers Thread Intelligence PhishDestroy Community | |||||||
source
https://forum.bits.media/index.php?/topic/2132560-четыре-сайта-одна-помойка/
https://forum.bits.media/index.php?/topic/233841-вызывает-опасения-comcash-анонимный-обмен-криптовалют-✅-нет-kyc-✅-низкий-aml/page/6/
https://forum.bits.media/index.php?/topic/2123402-вызывает-опасения-криптообменник-без-верификации-aml-и-kyc-secrex/page/6/#comment-2536803
https://bitcointalk.org/index.php?topic=5494387.20
https://bitcointalk.org/index.php?topic=5598351
Trust Rating
related to the category
I did some digging — there's actually a fair amount of material on this case beyond the two forums, including a technical audit that came out a whole three months before the hack.
The main find is an audit dated August 3, 2026, which got torn apart on Exp***t and then republished by on**n.as and the analytics outlet IntelHawk. According to it, ComCash isn't a standalone service but one of at least ten brands run by a single operator — one who'd already been banned on Exp***t as a scammer. The authors claim that all the domains send email from a single IP (the SPF, MX and mail subdomains all resolve to the same host at a Seychelles-based hoster), that comcash.cc had a build-manifest sitting in plain sight with entry points for seven brands at once (one Laravel project with switchable themes), that each domain was hosting the others' files, and that a check of the /api/get/directions endpoint matched 81 out of 81 deposit wallets. There's a Telegram tie-in too: the description of ComCash's AML bot pointed to the same support account as the banned service, and one of the brands' sites advertised the exact same Tor address as Barbados Exchange. The writeup also claims that the "independent" monitoring site AntiSwap actually belongs to the same network — the ComCash and Secrex names are hardcoded into its code, and four of its eleven "featured" exchangers belong to the cluster.
On Nul***B, a separate thread popped up on October 30 about the Barbados hack, listing exactly what got out: customers' email addresses, transaction data, IPs, dates of birth and more. The archive links in the thread lead to file-sharing sites — I didn't open them. Also worth flagging: the defacement hit not only comcash.cc and comcash.exchange but secrex.io as well — at the time of checking, all three were serving the same swapped-out page, with a mocking text in place of the exchanger plus links to download the database, the source code and the "playbook".
PhishDestroy had flagged comcash.cc as far back as August 4, 2026, with a critical score of 78/100, four out of 89 detections on VirusTotal and an "imitation" label; their last recorded successful hit on the site is dated October 29 at 11:51 UTC — literally just a few hours before the pages got replaced.
The funniest part is KYCnot.me. As of my check, ComCash's card is still up there, and the security section straight-up says no incidents or warnings have been recorded and that nobody on the team ever verified the listing. So a service with a leaked customer database and a defaced site formally still counts as perfectly private and trustworthy. The card on AntiSwap opens without warnings too — just reviews — and on pro-change.ru the exchanger is listed as three years old with zero complaints, plus a "Not active" status.
A review on bitok.blog had already pointed out back in May 2026 that the monitoring sites give it a three-year track record, even though the domain was registered on October 10, 2025, and the rep's forum posts are dated before the domain's registration; the takeaway there was cautious — the service apparently started up earlier under a different name, but the date mismatch doesn't exactly inspire trust. A second piece on the same site is way blunter and points to copy-paste positive reviews.
source
https://web.archive.org/web/20261103091342/https://onion.as/754
https://web.archive.org/web/20261103091545/https://onion.as/793
https://ghostarchive.org/archive/KxvCw
https://ghostarchive.org/archive/RHSsR
https://web.archive.org/web/20261103092818/https://intelhawk.ai/elementor-2920/
https://web.archive.org/web/20261104052602/https://www.pro-change.ru/comcash
https://web.archive.org/web/20261103093313/https://bitok.blog/comcash-cc-otzyvy
https://web.archive.org/web/20261104054106/https://bitok.blog/comcash-scam
https://web.archive.org/web/20261104054350/https://phishdestroy.io/domain/comcash.cc/
https://archive.ph/5rKhw
https://kycnot.me/service/comcash