
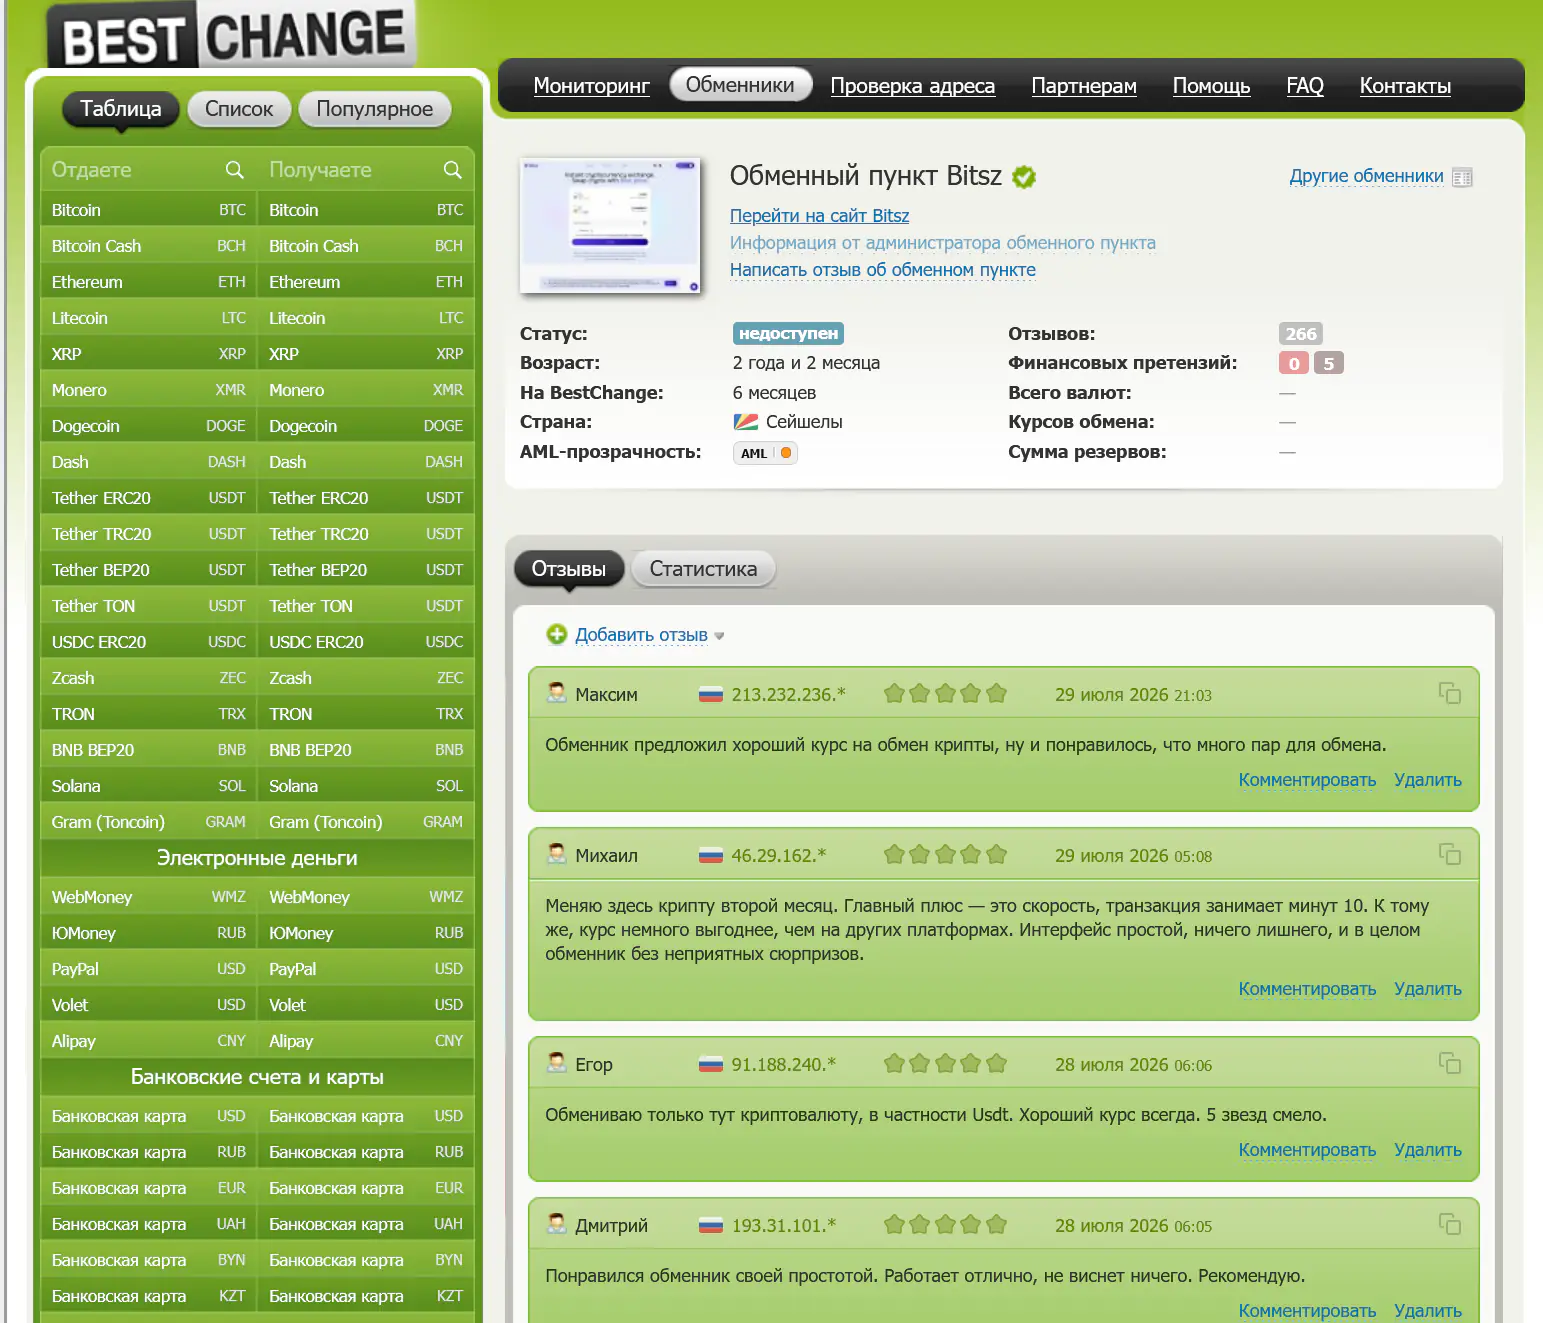
A serious conflict has unfolded on the forum between a client and the crypto exchanger Bitsz, which escalated into a real detective story with accusations of personal data leaks.
According to user hulkyjamkal, it all began when the exchanger blocked his transaction on contrived grounds and refused to return the funds. The service provided the results of an AML check indicating problems.
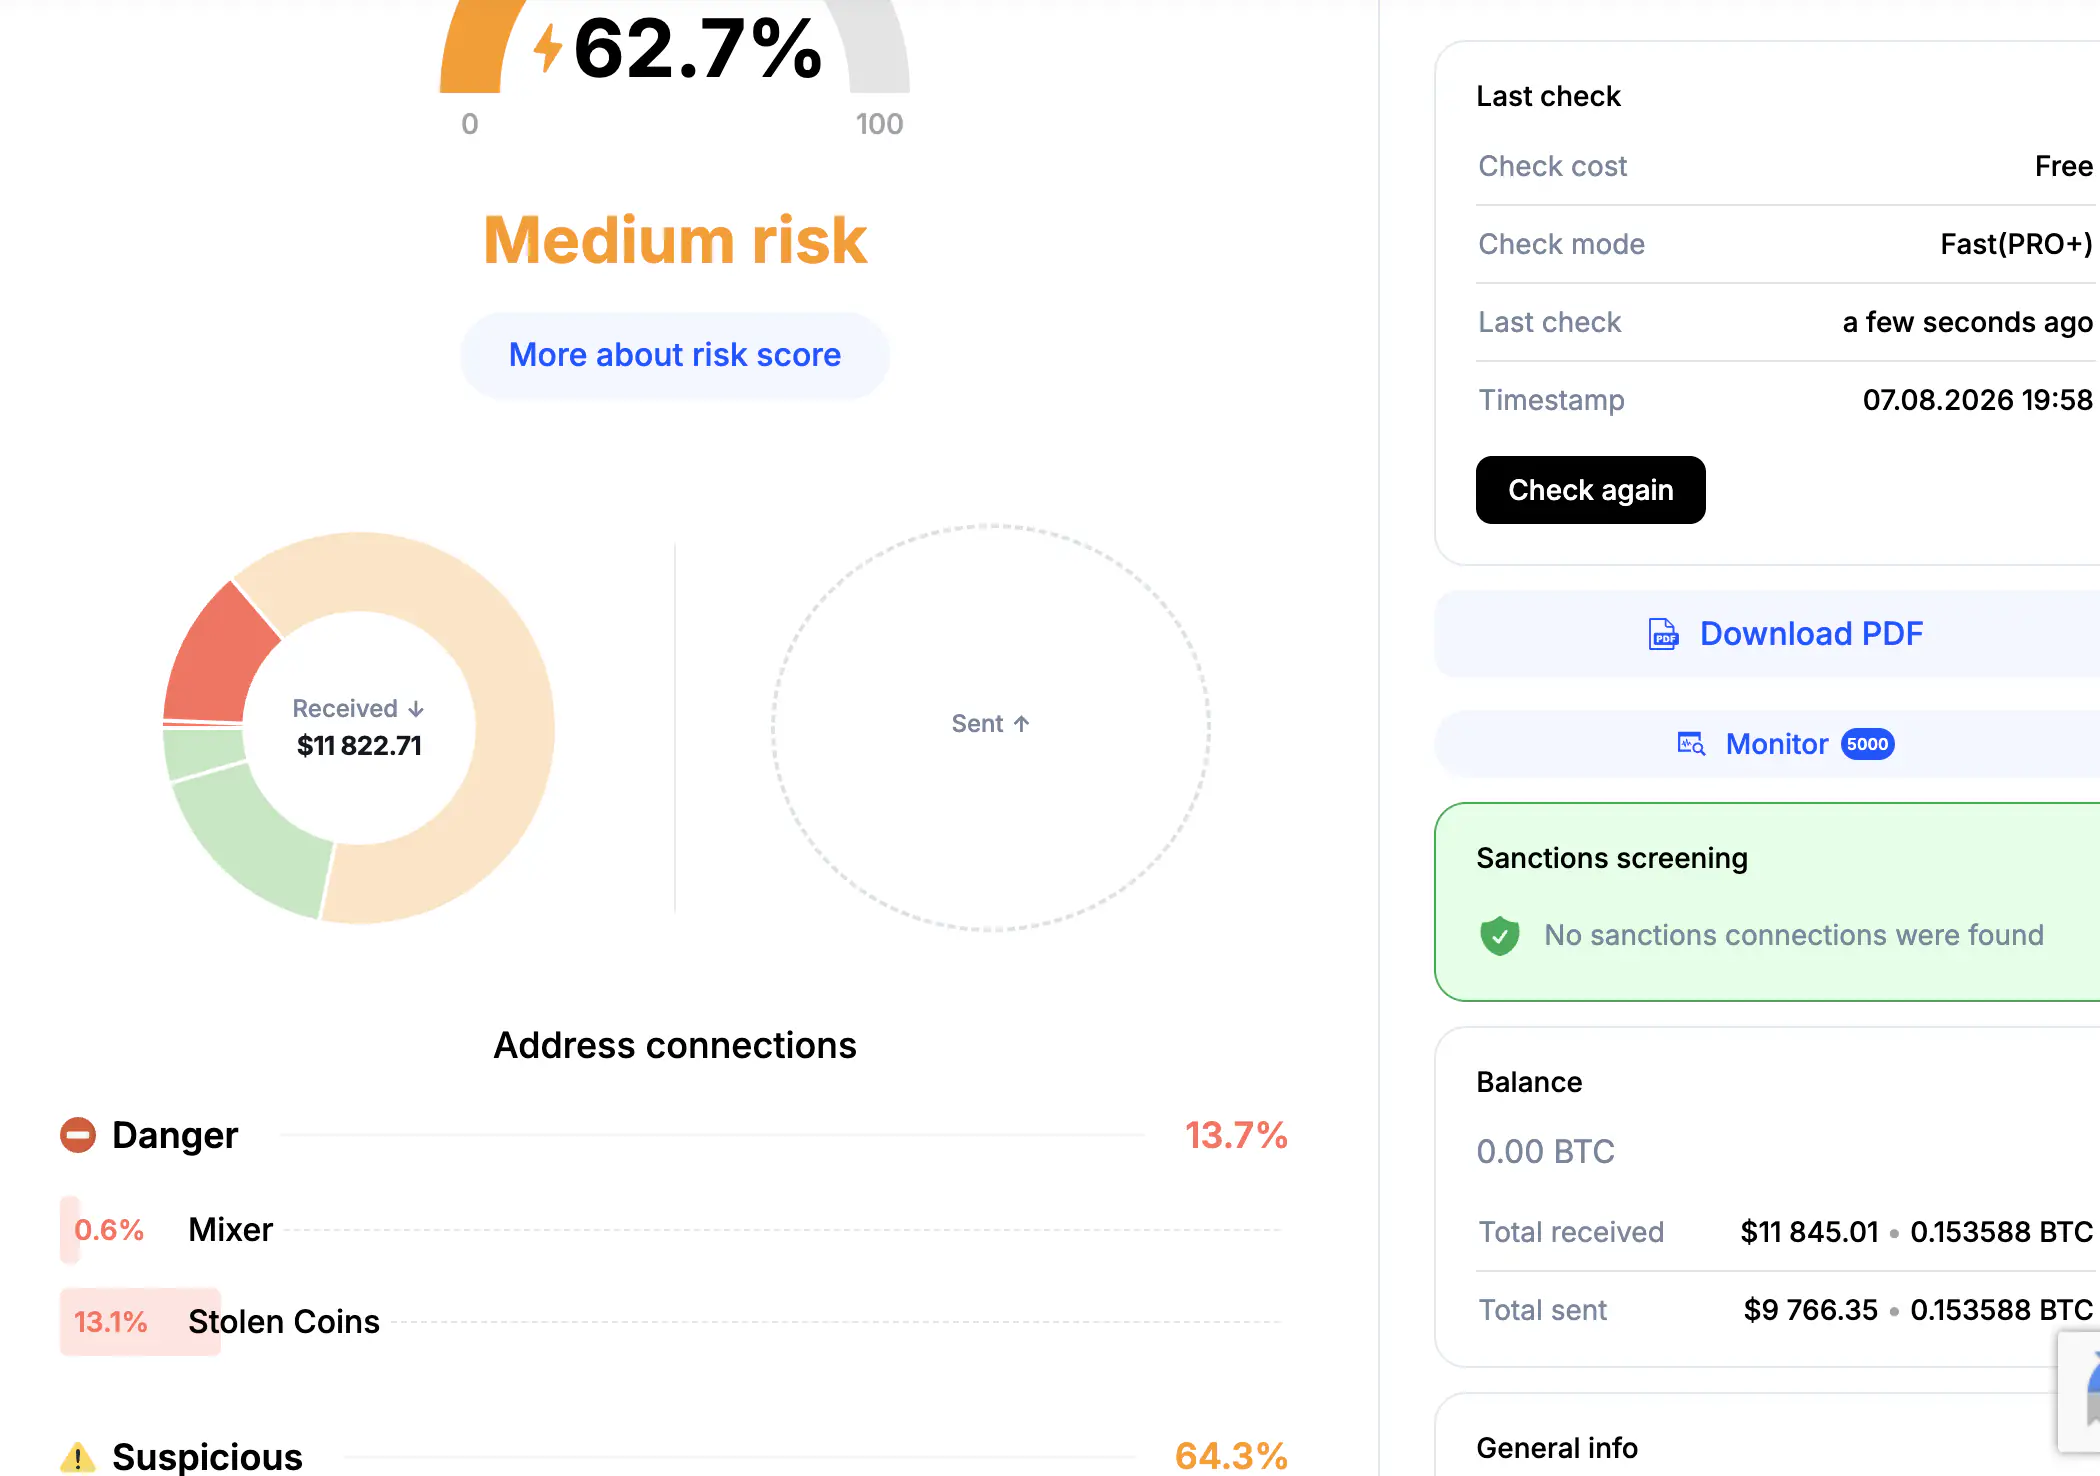
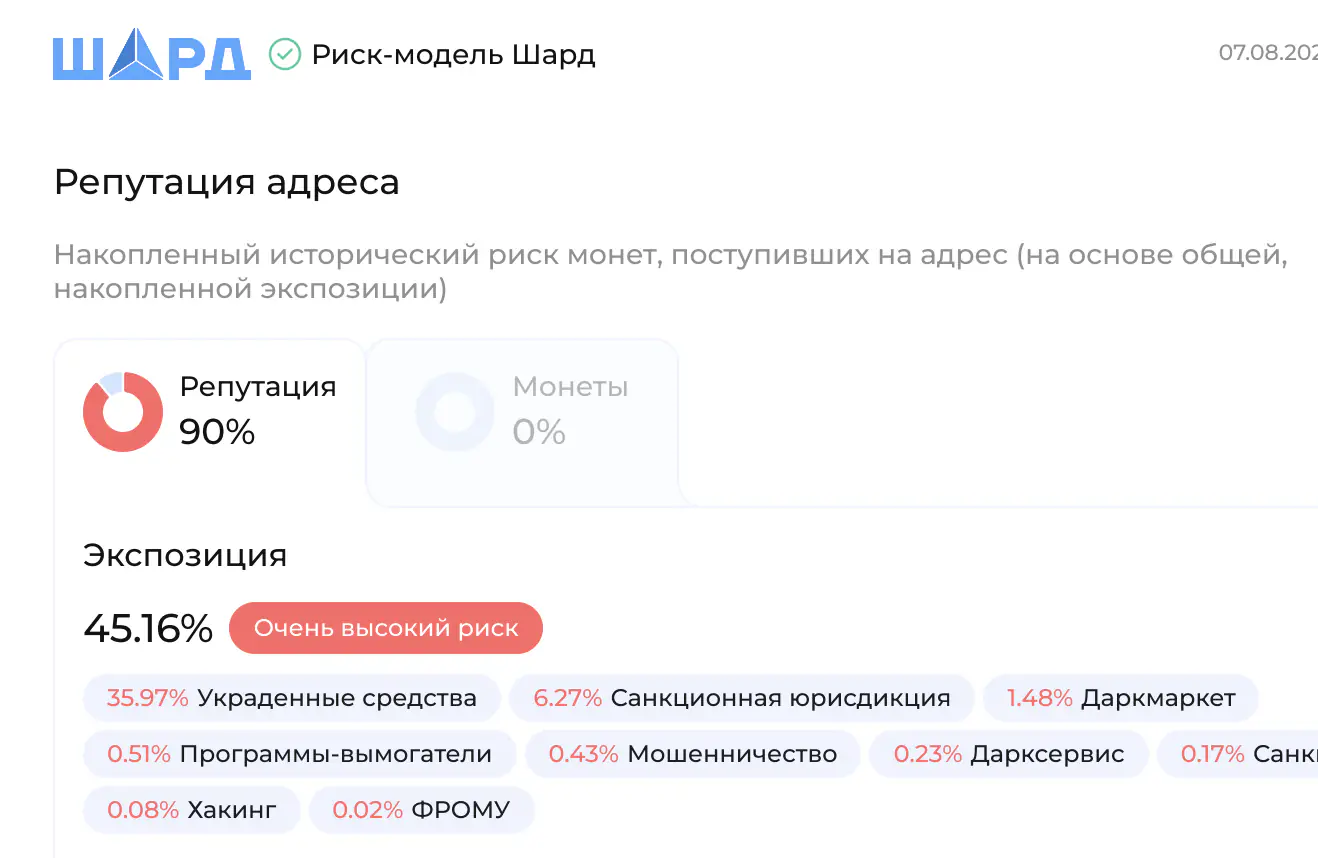
However, the user independently checked the coins through the very service that Bitsz references, and the result turned out to be completely "green".
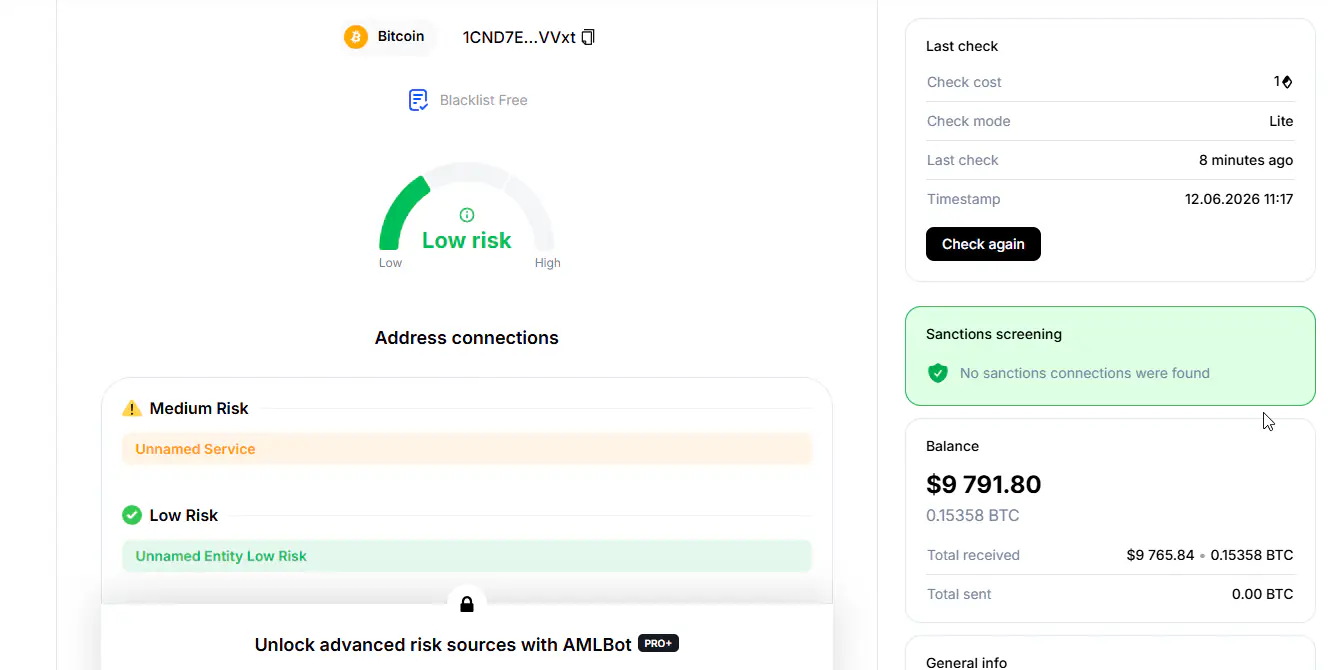
The exchanger's representative countered by stating that the crypto had been frozen by their liquidity provider — the Bybit exchange — due to "Stolen Coins" risk labels, and that passing a verification was required to unlock it. But the user quickly pointed out inconsistencies: the AML provider used by the exchanger produces different results on different pricing tiers, and the risk labels are as far as 15+ hops away, which is not grounds for a freeze.
The most interesting part began when facts of privacy violations came to light. According to user hulkyjamkal, he has direct evidence that his data was leaked to third parties. The email containing his full name and bank name was sent to him by... BestChange monitoring itself. It turned out that this information had been passed to them by the Bitsz exchanger. The user notes that this brazenly violates clause 13 of the exchanger's own privacy policy, as well as clause 10 of BestChange's own "Participation Terms". Moreover, as the client stated, the monitoring administration took no action against Bitsz, and the exchanger continued to operate.
The exchanger's attempts to justify itself by claiming that the data was passed to BestChange solely to help the client look unconvincing. The user drew attention to the fact that Bitsz publicly admitted to violating its NDA with the Bybit exchange: initially, they cited a non-disclosure agreement and refused to show screenshots of the requests, and then they themselves leaked them to third parties.
There was also an exposure of fake review inflation. The user attached archives showing that fake positive reviews about the service continued to be published even on days when the exchanger's website was physically inaccessible and removed from monitoring.
According to user hulkyjamkal, at the moment the exchanger has been ignoring his requests for information about the personal data operator for two months now, which directly violates its own rules. The client is convinced that stalling for time, leaking data, and using legally void rules is nothing short of outright fraud, and that the service is simply hoping to appropriate someone else's funds over time.
url
| domain | explore | registered | registrar | abuse email | score | average | |
|---|---|---|---|---|---|---|---|
| bitsz.io | May 20, 2024 | NameSilo, LLC | [email protected] | 30/100 | 30.0 | ||
| Blacklist: NoCoin Hexxium QuidsUp URLhaus FadeMind MetaMask Phishunt Badd-Boyz BlackBook CoinMiner OpenPhish ThreatFox TweetFeed PhishRadar Scam Block Abuse Block Phishing DB ScamSniffer PhishDestroy Malware Block Phishing Army Toxic Domains Filters Heroes GlobalAntiScam Phishing Block Pi-hole Trojan Scam Blocklist Fraud Blocklist Pi-hole Malware Crypto Blocklist Pi-hole Phishing Ransomware Block CyberHost Malware Pi-hole Malicious Pi-hole C2 Servers Thread Intelligence PhishDestroy Community | |||||||
source
https://forum.bits.media/index.php?/topic/2117460-подозревается-в-aml-терроризме-обменник-bitsz/page/7/#comment-2512488
https://archive.ph/XXvhV
https://archive.li/JZCSP
https://archive.li/Lk0XS
Trust Rating
related to the category