
On November 19, 2026, bitcointalk user examplens started a thread titled "Phishing and a new level of rudeness". The reason: another user, otcguardin, had opened a thread in the services section presenting his "privacy exchange" under the name b1ack Exchange. Domains in the signature: b1-exch[.]top and bl-exch[.]top, plus an onion address. In examplens's view, the design repeats one-to-one the exchanger b1exch[.]to / blexch[.]to that has long existed on the forum. In his words, "quite obvious that it is a phishing attempt".
The thread quotes otcguardin's own text: "financial privacy is not a crime", "no logs, no KYC, no JavaScript" swapping Bitcoin/ETH/XMR/DAI/USDT/LTC in minutes. In examplens's opinion, there is no point reading further — this is an attempt to impersonate a known service.
What the comments say
The Cryptovator left otcguardin negative feedback for impersonating b1exch — "established exchange here". In his view, scammers copied the original to confuse users both on the forum and beyond it. His advice is simple: always check the link when dealing with an instant exchanger.
logfiles called it a "bold attempt to promote a phishing scam" and also went to leave negative feedback. In his view, a type 1 flag is needed to protect the forum's newcomers and guests — and he asked examplens to raise it.
Coyster dug into the ecosystem. In his observation, privacy exchangers appear on the forum regularly, and as soon as one is burned, the next one shows up. "Hard to argue that they aren't run by the same syndicate" — but at least they usually change the domain, whereas here, in his view, they didn't even do that.
sunsilk recorded the outcome: the thread has been deleted. According to him, otcguardin's history turns up telegram contacts from services he promoted four years ago under different names. And in the latest thread — a month ago — he posted a link to a "directory" registered a month earlier, while claiming it had been launched in 2015 and "rebuilt last year". In sunsilk's opinion, any contacts and links from this user should be avoided.
What other sources say
The thing is, even the "original" b1exch[.]to is highly questionable in its own right.
On bitcointalk, a separate warning thread has been up since March 2026: "b1exch.to Exchange — honeypot setup [Warning: High-risk]". In the author's view, the verdict is: don't swap anything over $1,000, and it shows "all the markings of a long-con exit scam." In that same thread, individual commenters warn that "selective scam exchanges are selective, hence the name" — small amounts go through, large ones get taken. Whether these claims are true or false is unknown.
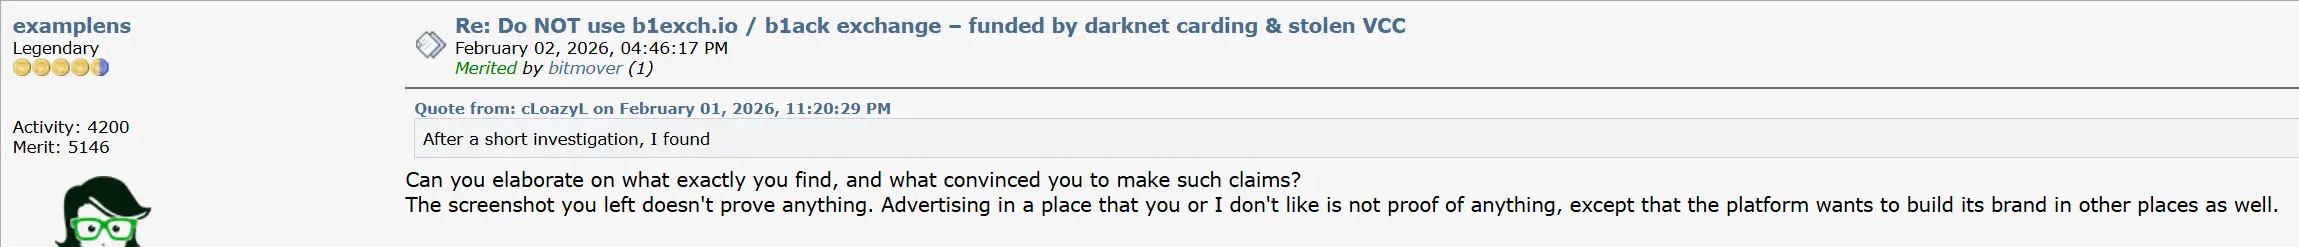
In February 2026, a separate user made the post "Do NOT use b1exch.to / b1ack exchange – funded by darknet carding & stolen VCC" — in his view, the platform is tied to darknet fraud, and using the service amounts to directly supporting scammers and carders. An amusing detail: in that thread, examplens himself responded skeptically — the screenshots, he said, prove nothing.
What it all adds up to
The design of a known exchanger has been copied. The domain is freshly registered. The thread was deleted by a moderator. Three negative trust feedbacks from Legendary users of the forum. Every point matches the description of a phishing impersonation recorded by The Cryptovator, logfiles, and Forsyth Jones.
No confirmed cases of losses on b1-exch[.]top / bl-exch[.]top could be found — the site is too new, and the thread was taken down quickly. Several complaints about the "original" b1exch[.]to itself, with accusations of a honeypot scenario and ties to darknet platforms.
| domain | explore | registered | registrar | abuse email | score | average | |
|---|---|---|---|---|---|---|---|
| blckexcrpdmau6y7teqxmf6yiyg7xn7qlphjeaxgyimxokz623w4tmqd.onion | None | None | None | 4/100 | 4.0 | ||
| Blacklist: NoCoin Hexxium QuidsUp FadeMind MetaMask Phishunt Badd-Boyz BlackBook CoinMiner OpenPhish TweetFeed PhishRadar Scam Block Abuse Block Phishing DB ScamSniffer PhishDestroy Malware Block Phishing Army Toxic Domains Filters Heroes GlobalAntiScam Phishing Block Pi-hole Trojan Scam Blocklist Fraud Blocklist Pi-hole Malware Crypto Blocklist Pi-hole Phishing Ransomware Block CyberHost Malware Pi-hole Malicious Pi-hole C2 Servers Thread Intelligence PhishDestroy Community | |||||||
| b1-exch.top | Sept. 7, 2026 | Tucows.com Co | [email protected] | 4/100 | 4.0 | ||
| Blacklist: NoCoin Hexxium QuidsUp FadeMind MetaMask Phishunt Badd-Boyz BlackBook CoinMiner OpenPhish TweetFeed PhishRadar Scam Block Abuse Block Phishing DB ScamSniffer PhishDestroy Malware Block Phishing Army Toxic Domains Filters Heroes GlobalAntiScam Phishing Block Pi-hole Trojan Scam Blocklist Fraud Blocklist Pi-hole Malware Crypto Blocklist Pi-hole Phishing Ransomware Block CyberHost Malware Pi-hole Malicious Pi-hole C2 Servers Thread Intelligence PhishDestroy Community | |||||||
source
https://bitcointalk.org/index.php?topic=5600389.0
https://bitcointalk.org/index.php?topic=5578194.0
https://bitcointalk.org/index.php?topic=5573204.0
Trust Rating
related to the category